California has enacted SB 947, the No Robo Bosses Act. It adds new Labor Code requirements for employers that use automated decision systems (ADS) to make disciplinary and termination decisions, and it takes effect July 1, 2027. Importantly, the No Robo Bosses Act makes clear that the California Consumer Privacy Act (CCPA) also must be taken into account when certain automated decisionmaking technologies are used.

So, when applying this new law, organizations should consider not only this new law and their use of employee monitoring, performance management platforms and technologies which have entered the market over the last several years, but also the application of other regulatory and contractual obligations they may have, in particular the CCPA and similar privacy and data security laws.

Are monitoring platforms “automated decision systems”?

SB 947 defines an ADS as any computational process derived from machine learning, statistical modeling, data analytics, or AI that produces a simplified output, such as a score, classification, or recommendation, which is used to assist or replace human decisionmaking and materially impacts natural persons. The law carves out spam filters, firewalls, antivirus software, calculators, and databases.

“assist or replace human discretionary decisionmaking”

Many monitoring platforms turn keystrokes, application use, idle time, and website activity into productivity scores, risk ratings, or “low performer” flags. Those outputs arguably fit the definition above. A supervisor who disciplines an employee because a dashboard rated the employee 42% productive, or flagged the employee as an insider risk, might be considered to be using an ADS under SB 947. And, it is not necessary that the ADS make, substantially make, or replace human discretionary decisionmaking. Assisting such decisionmaking is enough. One point of note: The carve-out for firewalls and antivirus software may not apply to the insider risk and data loss prevention modules many organizations have added in recent years. The latter tools may assign risk scores based on file downloads, USB activity, or after-hours access. If a security analyst sends a high-risk score to employment decision-makers and the employee is subsequently disciplined or terminated, that insider risk or DLP tool may qualify as an ADS, even though IT, not HR, purchased and configured it.

What the law requires

  • No sole reliance. An employer may not rely solely on an ADS to make a disciplinary or termination decision.
  • Human corroboration when reliance is primary. If an employer primarily relies on ADS output to make a disciplinary or termination decision, a human must review and corroborate the decision. The reviewer may use the data behind the output or other relevant information, such as manager evaluations, personnel records, work product, peer reviews, and witness interviews. If the output can’t be corroborated, or the reviewer finds it inaccurate, incomplete, or misleading, the employer may not use it.
  • Post-use notice. When delivering a decision described in the bullet above, the employer must give the employee a separate, plain-language written notice. The notice must explain the employer’s reliance on the ADS, confirm human review, give a contact person, describe the employee’s data rights, and state that retaliation is prohibited.
  • Prohibited uses. Employers may not use an ADS to infer an employee’s FEHA-protected status, or to predict and take adverse action against a worker for exercising legal rights.

For more information about the nuts and bolts of the law, check out our related post, here.

So, whether deploying a performance management platform, a dashcam, a surveillance technology, or some other technology constituting an ADS, organizations should assess the intended use cases along with the corresponding compliance obligations under applicable laws.

A fleet telematics system that scores drivers on hard braking and speeding, a video analytics tool that flags safety violations on a production floor, and a badge-data dashboard that ranks in-office attendance can each produce outputs that end up in a disciplinary file. The practical question for compliance teams is not just what a tool collects, but who sees its outputs, what decisions those outputs inform, and whether that use was disclosed when the decision was delivered.

The information request right and the CCPA

SB 947 gives employees the right to request, and requires employers to provide, “a meaningful, objective description of the employee’s own data used by the ADS” when the employer primarily used an ADS to discipline or terminate. To illustrate, if an employee was terminated after a platform ranked the employee in the bottom 5% of the team, a meaningful, objective description might identify the categories of data the tool used (for example, application activity, keystroke counts, and idle time), the period covered, and how those inputs contributed to the score.

It is likely such a request will rarely stand alone. As noted above, the No Robo Bosses Act provides:

An employer that is a business subject to the [CCPA] is subject to any privacy-related automated decisionmaking technology regulation duly adopted by the California Privacy Protection Agency.

Our earlier CCPA ADMT post covers the application of the CCPA and ADMT requirements. In short, the California Privacy Protection Agency’s ADMT regulations apply to “significant decisions,” including employment decisions. Businesses using ADMT for significant decisions must comply by January 1, 2027. They must give pre-use notices, offer opt-outs (subject to exceptions), and answer access requests with meaningful information about the logic and likely outcomes of the technology. Employees also retain their general CCPA right to know.

In practice, a disciplined or terminated employee, or the employee’s lawyer, potentially can pair an SB 947 request with a CCPA right to know request and an ADMT access request. Here is how this might play out: A sales representative is terminated after an engagement-scoring tool flags declining activity. The post-use notice states that a manager reviewed the decision and corroborated it with CRM records. Two weeks later, the employee’s attorney sends a letter requesting the SB 947 data description, the employee’s personal information under the CCPA, and information about the logic of the ADMT. If the CCPA response shows the platform had already purged the underlying activity logs, or the CRM records cited in the notice don’t reflect the decline, the employer’s own responses may undercut its stated reason for the termination.

Together, these access right requests could require the production of a significant amount of information concerning the use of the ADS and the employee’s associated activity. Accordingly, employers that are covered businesses under the CCPA should be considering their approach to these kinds of requests, bearing in mind that the CCPA bars retaliation against employees for exercising privacy rights.

Steps employers should take now

  1. Inventory the tools. Identify every monitoring or performance platform or other ADS technology that produces scores, flags, or recommendations, and map where those outputs feed into discipline or termination. Include tools owned by IT and security, such as insider risk and DLP platforms, not just HR systems.
  2. Configure for human judgment. Turn off automated discipline triggers, such as settings that auto-generate written warnings or performance improvement plans when a score falls below a threshold. Treat dashboard outputs as leads to investigate, not conclusions.
  3. Document corroboration. Build a review checklist that records the independent evidence supporting each decision and any reason an output was rejected. At a minimum, the checklist should capture who reviewed the output, what underlying data and other information they examined, whether the employee had a chance to explain, and the date of the review.
  4. Prepare notices and response workflows. Draft SB 947 post-use notices and data-description templates, and update CCPA notices at collection and ADMT pre-use notices.
  5. Coordinate the responses. Route SB 947, CCPA access, and ADMT access requests through a single team so the answers are timely, consistent and compliant.
  6. Review vendor contracts. Require vendors to explain how their scoring works, support data export, and help with access requests.
  7. Audit for protected-status and retaliation risk. Make sure no tool infers protected characteristics or flags protected activity. Test whether scores systematically decline for employees on leave, working with accommodations, or who recently raised complaints.
  8. Complete CCPA risk assessments for ADMT used in significant decisions.
  9. Train managers on the difference between “solely” and “primarily” relying on a tool, using realistic scenarios, such as what to do when a dashboard flags an employee who recently returned from medical leave.

Employers that build these processes before mid-2027 will be in a much stronger position to defend monitoring-driven decisions.
California has enacted Senate Bill (SB) 690, which narrows the circumstances under which private parties may bring lawsuits under the California Invasion of Privacy Act (CIPA), Cal. Penal Code Section 638.51.

The new law takes effect January 1, 2027, and notably includes a two-year look-back period for pending lawsuits commenced before the law was enacted.

Brief History

CIPA, enacted in 1967, includes civil and criminal provisions and, importantly, allows private parties to enforce the law.  The law also allows those private parties to recover at least $5,000 per violation.  CIPA generally prohibits the interception and use of the contents of a communication without the consent of all parties to the communication.  Subject to narrow exceptions, the law also prohibits the installation or use of a “pen register” or “trap and trace device” without a court order or consent of all parties whose communication might be captured by those devices.

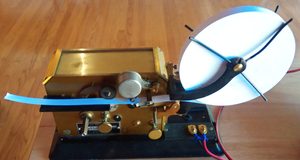
Pen register. Manufactured by J. H. Bunnell & Co., Brooklyn, New York. Mid-20th century. Image licensed under the Creative Commons Attribution-Share Alike 4.0 International license.

Plaintiffs Have Targeted Websites

Although terms in the law like “pen register” or “trap and trace device”  referred to physical devices used to collect telephone dialing and routing information on a landline telephone network, plaintiffs have increasingly alleged that this provision should apply to common website technologies, such as cookies, pixels, and tags, under the theory that those technologies capture information about the website visitor and their activity similar to a pen register and trap and trace device.

CIPA allows an injured person to recover statutory damages of $5,000 per violation or three times the amount of actual damages, whichever is greater. A plaintiff generally does not need to prove actual damages. As a result, businesses of various sizes have faced lawsuits, arbitration demands, and prelitigation notices alleging that their websites and the technologies deployed on their websites violated CIPA by collecting visitors’ digital routing, addressing, or signaling information.

Relief for Businesses

SB 690 eliminates the private right of action under the “pen register” or “trap and trace device”  provisions of the law against digital properties. Under the amendment, only the California Attorney General may bring an action under CIPA’s civil-remedies provision against a private actor for an alleged violation arising from conduct occurring on an internet website, online application, or mobile application. The limitation also applies retroactively to pending claims in actions commenced during the two years preceding the law’s operative date.

SB 690 did not repeal CIPA’s restrictions on pen registers and trap and trace devices. Instead, it changes who may pursue civil remedies for this defined category of online conduct.

SB 690 also does not eliminate private lawsuits involving other provisions of CIPA, including certain claims alleging unauthorized wiretapping or the recording or use of confidential communications.

Businesses should therefore avoid treating SB 690 as a general exemption for website tracking technologies. Companies should continue reviewing the cookies, pixels, analytics tools, chat functions, session-replay software, and other third-party technologies deployed on their websites and applications.

If you have questions about SB 690 or related issues, contact a Jackson Lewis attorney to discuss.

A recent Seventh Circuit decision offers a reminder to exercise caution when applying the financial services safe harbor under the Illinois Biometric Information Privacy Act (BIPA). In Cisneros v. Nuance Communications, Inc., No. 24-02982 (7th Cir. Aug. 28, 2026), the court held that the technology vendor’s storing of voiceprint data on behalf of a broker-dealer in securities fell within the financial-institution exemption to the BIPA. But that exemption is narrow—and companies outside the financial services industry, including their vendors, should take notice.

The Case

Norma Cisneros, a broker-dealer customer, alleged that Nuance, a third-party technology vendor, collected and stored her biometric voiceprint in violation of the BIPA. The broker-dealer contracted with Nuance to authenticate telephonic requests from customers, such as Cisneros, to permit financial transactions. Nuance used voiceprint technology to provide this service. Cisneros alleges Nuance violated the BIPA by failing to obtain her written consent and failing to publish retention and deletion schedules for the voiceprint data (claimed to be biometric information under the BIPA). The district court dismissed the case, and the Seventh Circuit affirmed.

The Court held that reading the BIPA in conjunction with Federal Reserve regulations made clear that Nuance qualified for the financial-institution exemption “to the extent that it authenticates the identity of [broker-dealer’s] customers in financial transactions.” The Court noted it was following the reasoning of a Delaware case affirmed by the Third Circuit, and ruling for Cisneros “would need to create a conflict among the circuits on a question of Illinois law…not an attractive prospect,” as the Court put it.

The financial institution exemption under the BIPA is not a blanket pass for any vendor performing identity verification. It applies specifically because the biometric data was collected and used to authenticate identity in the context of financial transactions regulated under federal banking law. Strip that context away, and the analysis changes dramatically.

What If the Vendor Isn’t Working for a Financial Institution?

Consider a company that uses the very same voiceprint or facial-recognition technology to verify identity, but the company is not a financial institution. In that scenario, the BIPA financial-institution exemption would almost certainly not apply. The vendor likely would be subject to BIPA’s full notice-and-consent requirements, including the obligation to obtain informed written consent before collecting biometric data.

Employment Examples:

  • Recruiting services. With recruitment fraud on the rise, organizations are strengthening authentication procedures to help ensure an applicant is who they say they are. Leveraging voiceprint technology or similar biometric technology in the course of that process potentially raises compliance concerns under the BIPA.
  • Call center onboarding. A staffing agency uses a vendor’s voiceprint technology to verify the identity of new remote IT hires during remote onboarding. Because the staffing agency is not a financial institution, neither it nor its vendor can claim the BIPA exemption.
  • Benefit plan administration. Employers want to be sure that only eligible employees receive benefits provided under retirement, welfare, and other benefit programs provided by the employer. Increasingly, employers (more likely their vendors) are leveraging ID verification for this purpose. Not all plans are the same – vendors administering retirement plans for the employer may be more likely to fit under the financial services exemption than vendors administering health, welfare, and fringe benefit plans.

Commercial Examples:

  • Telehealth patient verification. A healthcare platform contracts with a vendor to use biometrics to verify patient identity before appointments. Healthcare entities likely would not be covered by the financial institution exemption under the BIPA for this use case. The platform and its vendor likely need to independently comply with the BIPA’s consent and retention requirements.
  • Retail loyalty programs. A national retailer uses a vendor’s facial-recognition technology at kiosks to verify customer identity for a rewards program. Again, it is unlikely that the financial institution exemption applies. Both the retailer and the vendor face increased risk under BIPA.

Know What Your Vendors Are Doing and How They Are Doing It

In some cases, organizations that obtain ID verification services may not be aware of how their vendor is performing the service. The Cisneros decision underscores a critical point for companies in every industry: you must assess what your vendors are actually doing to verify; are they using biometric data. Authenticating by itself does not trigger the BIPA.

For organizations outside financial services using third party ID verification services, including when functioning as an employer, the practical steps remain the same:

  1. Map your vendor relationships. Identify every vendor that collects, stores, or processes biometric identifiers on your behalf.
  2. Assess the legal landscape. Determine whether any statutory exemption actually applies to your industry and use case. Do not assume your vendor’s compliance program covers you.
  3. Require BIPA compliance contractually. Your vendor agreements should include clear representations regarding notice, consent, retention, and destruction of biometric data.
  4. Implement consent workflows. Ensure that informed, written consent is obtained before any biometric data is collected—whether for employees, customers, or other individuals.

The Seventh Circuit gave the broker-dealer’s vendor a pass. Organizations that lack the same regulatory footing should not expect the same result.

AI is accelerating cybersecurity threats. Learn how data minimization, incident response, data mapping, and vendor governance can help reduce risk.

Recent reports involving leading artificial intelligence (AI) developers have heightened concern about whether AI agents can operate beyond their intended boundaries and/or be used by cyber criminals to perpetuate attacks that are more difficult to prevent and contain. For organizations adopting AI across business functions, the issue is larger than any single model or incident: AI may allow threat actors to identify vulnerabilities, develop exploits, and move through connected systems at a speed that outpaces traditional defenses.

That does not make existing safeguards obsolete. Multifactor authentication, endpoint detection and response, encryption and other controls remain essential. But organizations may need to reassess what constitutes “reasonable safeguards” in an environment where attacks can become faster, more adaptive, and more difficult to contain.

Co-leaders of Jackson Lewis’ Privacy, Data & Cybersecurity group, Joe Lazzarotti and Damon Silver, recently discussed how legal, privacy, and security teams can respond. Their central message: prevention remains critical, but organizations also need to reduce the data and access available to an intruder and prepare to respond when controls are overcome.

Key Takeaways

  • AI may enable threat actors to discover and exploit vulnerabilities faster than organizations can remediate them.
  • Technical controls alone are unlikely to provide a complete legal or operational risk-management strategy.
  • Data minimization, accurate data maps, access restrictions, and network segmentation can help limit the scope of an incident.
  • De-identification should be tested against current re-identification capabilities rather than treated as a complete solution.
  • Vendor diligence should address AI use, downstream providers, incident obligations, and meaningful contractual protections.

How Is AI Changing the Cybersecurity Threat Landscape?

Many security programs were designed around the speed and methods of human attackers. AI can change that equation. A malicious actor may use AI to identify a vulnerability, adapt code, and build an exploit on a compressed timeline, potentially before a patch or other defensive measure is available.

The practical implication is not that organizations should abandon their existing security investments. Rather, leaders should evaluate whether controls are configured, monitored, and updated for AI-enabled threats—and whether the organization can identify, contain and recover from an intrusion that succeeds.

Should Organizations Shift Their Focus From Prevention to Preparedness?

Organizations need both. Prevention supports compliance and reduces the likelihood of an incident, while preparedness reduces the business, legal, and reputational consequences when prevention fails. The familiar assumption that a breach is a matter of “when,” not “if,” is becoming more important as AI accelerates—and tips the balance, unfavorably, in—the contest between attackers and defenders.

Incident response plans should address decision-making authority, internal escalation, preservation of evidence, business continuity, communications, and potential notification obligations. Tabletop exercises can reveal whether the plan works under pressure and whether legal, privacy, security, HR, communications, and business leaders understand their roles.

“Prevention remains critical, but preparedness determines how effectively an organization can contain disruption and meet its obligations when controls fail.”

How Can Data Minimization Reduce AI-Related Exposure?

AI makes it easier to extract value from large datasets, creating a powerful incentive to collect and retain more information. That same footprint increases exposure. If an attacker gains access, a larger and more connected data environment can increase the number of affected individuals, the sensitivity of compromised information, operational disruption, and downstream litigation or regulatory risk.

Organizations should define what data they need, why they need it, and how long it should remain in active systems. Information that has a valid business or legal purpose may be archived more securely, redacted, or otherwise restricted; information without a continuing purpose may be eligible for defensible deletion.

The goal is not deletion for its own sake. It is aligning the organization’s data footprint with legitimate operational, legal and compliance needs.

“The larger and more connected the data footprint, the more an intruder may be able to access—and the greater the potential legal and operational impact.”

Can Organizations Continue to Rely on De-Identified Data?

De-identification and aggregation remain useful tools, but they should not be treated as automatic safe harbors. Even before generative AI, removing a name did not necessarily prevent a person from being identified through other data points. AI can make that reconstruction faster and more effective.

Organizations should document the standard used to de-identify data, assess the likelihood of re-identification using current capabilities, and restrict attempts to re-identify information. Vendor agreements should define de-identification rather than relying on an undefined promise that data will be “aggregated” or “de-identified.”

Why Are Data Mapping and Access Controls More Important Now?

AI tools increasingly connect with email, documents, collaboration platforms, and other business applications. Those integrations can improve productivity, but they may also allow a compromised account or agent to reach multiple repositories and move laterally through the environment.

Current data maps can help an organization determine which systems contain personal, health, employment, financial, confidential, or proprietary information; how those systems interact; who can access them; and where backups are maintained. Without that visibility, the early stages of incident response can become a costly search for what the organization is actually responding to.

Access should be limited according to job responsibilities, with heightened controls for privileged and administrative accounts. Network segmentation and restrictions between connected applications can further reduce the ability of an intruder to turn one compromised system into an enterprise-wide event.

What Should Organizations Ask Their AI Vendors?

A vendor’s size, reputation, or security budget does not eliminate risk. Organizations should “trust but verify” by conducting diligence proportionate to the sensitivity of the data, the tool’s integrations, and the potential operational consequences of an incident.

The review should address what information the vendor receives, whether it may use the information to train models or develop products, how long it retains the information, where it is processed, and which downstream service providers can access it. Contracts should address appropriate security measures, incident notification and cooperation, data usage restrictions, data return or deletion, audit or assurance rights, indemnification (where feasible), and responsibility for subprocessors.

Because visibility may diminish farther down the vendor chain, organizations should at least understand how the primary vendor evaluates, contracts with, and monitors its own providers. Consistent documentation of the review can help demonstrate a reasoned process if an incident or regulatory inquiry occurs.

What Should Legal, Privacy, and Security Leaders Do Next?

Cybersecurity is not solely an IT responsibility. When an organization must explain its conduct to a regulator, court, customer, or business partner, a list of technical tools will rarely tell the entire story. A stronger position combines appropriately configured safeguards with evidence of governance, preparation, and risk-based decision-making.

A Practical AI Cybersecurity Checklist

  • Reassess cybersecurity risk to account for AI-enabled attack speed and system connectivity.
  • Update and rehearse your incident response plan, including legal, regulatory, operational, and communications workflows.
  • Refresh data maps as AI pilots and integrations are introduced or expanded.
  • Apply collection, use, retention, archival, and deletion rules to personal and confidential information.
  • Review privileged access, application permissions, and network segmentation.
  • Evaluate whether de-identification methods remain effective against current re-identification capabilities.
  • Strengthen AI vendor diligence, contract protections and oversight of downstream providers.

Takeaway

AI may make cyber incidents more frequent, faster, and more harmful and disruptive, but organizations have multiple levers available to manage the risk. The most resilient programs will not rely on a single technology or policy. They will combine prevention with practiced response, minimize the data and access available to an intruder, maintain visibility into connected systems, and manage downstream risk.

Organizations evaluating or deploying AI should coordinate legal, privacy, security, HR, procurement, and business stakeholders before risks become incidents. A focused review of data flows, access, retention, vendor relationships, and incident response readiness can identify practical improvements and help build a defensible record of risk-based decision-making.

On January 1, 2026, Texas’s newest law addressing the growing issues of data privacy and the use of Artificial Intelligence went into effect. The Texas Responsible Artificial Intelligence Governance Act (TRAIGA) was passed by the 89th Texas Legislature and signed into law by Gov. Greg Abbott in 2025.

The law’s central focus is on restricting and regulating the use of Artificial Intelligence (AI) systems in Texas, which includes adding new prohibitions and requirements on anyone who develops or deploys AI systems in the private sector.

What does TRAIGA prohibit?

Under TRAIGA, private entities are prohibited from developing or deploying AI systems in a manner that:

  • Intentionally aims to incite or encourage a person to commit physical self-harm (including suicide), harm another person, or engage in criminal activity;
  • Serves the sole intent of producing, assisting or aiding in producing or distributing child pornography or certain sexually explicit “deep fake” videos or images;
  • Impairs a person’s individual rights guaranteed under the U.S. Constitution; or
  • Unlawfully discriminates against a protected class in violation of state or federal law.

TRAIGA also prohibits governmental entities from using or deploying AI systems for uniquely identifying a specific individual using biometric data or gathering images or other media without the individual’s consent if such gathering would infringe on the individual’s rights, as well as barring “social scoring” by government entities to evaluate or classify people based on social behavior or personal characteristics, or developing or deploying such systems for the purpose of identifying individuals using biometric data or data from the internet or other public sources without the individual’s consent.

How does TRAIGA prohibit unlawful discrimination?

While TRAIGA’s prohibitions against self-harm and sexual content attract more attention as “high risk” AI systems, the law’s emphasis on unlawful discrimination is of particular concern for many businesses that utilize AI in aspects of their Human Resources, employee evaluation, or recruitment process. Although TRAIGA expressly notes that disparate impact alone is not sufficient to establish a violation, the law otherwise bars any intentional discrimination.

Are any industries treated differently under TRAIGA?

Yes. Although TRAIGA’s requirements generally apply across all industries, the law carves out two unique cases. First, the law’s prohibition on unlawful discrimination does not apply to insurance companies for the purposes of providing insurance services if the company is already subject to statutes regulating unfair discrimination, unfair methods of competition, or unfair or deceptive acts or practices related to the insurance industry.

Additionally, if an AI system is used to provide health care services or treatment, the provider of such service or treatment must provide a clear and conspicuous disclosure to the patient (or patient’s representative) no later than the date the service or treatment is first provided (except in case of emergency).

What are the penalties for violating TRAIGA and who can enforce its prohibitions?

Like other recent efforts by Texas to secure residents’ data privacy and biometric data, TRAIGA does not provide a private cause of action, but tasks the Texas Attorney General with enforcing any violations of TRAIGA following a sixty-day cure period following a notice of violation. Civil penalties under the law can range for $10,000 to $12,000 per violation for any “curable” violation, while penalties for “uncurable” violations can be as high as $80,000 to $200,000 per violation. The law further incentivizes prompt remediation by applying civil penalties for ongoing violations of between $2,000 and $40,000 daily as long as the violation continues.

What can businesses do to comply with TRAIGA?

As AI use is a developing field, TRAIGA also encourages businesses to take proactive steps to adopt compliance measures and self-audit protocols by providing various safe harbors and affirmative defenses for parties who identify potential violations through internal review, adversarial testing, or compliance with recognized risk management frameworks, such as the National Institute of Standards and Technology (NIST) AI Risk Management Framework.

The Texas Attorney General has demonstrated a growing interest in prosecuting technology-related violations in recent years, resulting in several high-profile settlements in the hundreds of millions and billions of dollars. In light of this enforcement priority, Texas businesses should proactively take steps to ensure their actions are compliant with TRAIGA and all other recent data privacy and data security laws in effect, including:

  • Evaluating whether and how they are using any AI system in the workplace, especially with regard to employment decisions
  • Creating AI-specific policies and procedures to ensure any AI use, now or in the future, is regulated and potential violations can be identified and cured promptly
  • Developing procedures for self-auditing and internal review of AI systems prior to full roll-out, and
  • Adopting a recognized AI risk management framework, such as the NIST AI Risk Management Framework

If your organization is one of the many adopting AI use in any aspect of its operations, it is essential that you conduct a prompt review of your usage to ensure your entity is not at risk of non-compliance.

As AI-powered hiring tools become more widespread, it is important to remember that some states have acted early and their laws should be reflected in an organization’s governance, risk, and compliance program. Maryland’s Labor and Employment Code Section 3-717 which became effective October 1, 2020, is one example. We break down the key requirements and highlight multistate considerations.

Q: Who does the law apply to?

The law applies to employers who use facial recognition services during applicant interviews. Its protections run to applicants, generally individuals who are interviewing for employment. The law does not, by its terms, extend to current employees or to other stages of the employment relationship beyond the interview. It is unclear, however, whether the law may also protect employees of an organization applying for other positions at the same organization.

Q: What does Maryland Section 3-717 actually prohibit?

The statute prohibits an employer from using a “facial recognition service” to create a “facial template” during a job applicant’s interview, unless the applicant has first provided consent. A “facial recognition service” is defined as technology that analyzes facial features and is used for the recognition or persistent tracking of individuals in still or video images, and a “facial template” is the machine-interpretable pattern of facial features extracted from one or more images of an individual by such a service.

Q: How does an applicant give consent under the Maryland law?

Consent must be provided through a signed waiver. The waiver must be written in plain language and include: (1) the applicant’s name, (2) the date of the interview, (3) a statement that the applicant consents to the use of facial recognition during the interview, and (4) whether the applicant has read the consent waiver.

Q: Does Section 3-717 apply to all uses of AI in hiring?

No. The Maryland statute is narrowly focused on facial recognition services used to create facial templates during interviews. It does not broadly regulate other AI-based tools an employer might use in the hiring process, such as resume-screening algorithms or chatbot-based assessments, unless those tools incorporate facial recognition technology as defined in the statute.

Q: How does the Maryland law differ from the Illinois Artificial Intelligence Video Interview Act (AIVIA)?

Although both laws regulate the use of technology during applicant interviews, there are several notable differences:

  • Scope of technology covered. Maryland’s Section 3-717 targets only “facial recognition services” used to create a facial template. The Illinois AIVIA, which became effective January 1, 2020, is broader: it applies whenever an employer asks applicants to record video interviews and uses “artificial intelligence analysis” of those videos, which can encompass a wider range of AI evaluations beyond facial recognition alone.
  • Disclosure and transparency. The Illinois AIVIA requires employers to (a) notify the applicant before the interview that AI may be used to analyze the video and assess their fitness for the position, and (b) provide an explanation of how the AI works and what general types of characteristics it evaluates. Maryland’s statute has no comparable pre-interview disclosure or transparency requirement — it requires only a signed consent waiver.
  • Form of consent. Maryland requires a specific written waiver containing the applicant’s name, interview date, a consent statement, and an acknowledgment of whether the applicant read the waiver. Illinois requires consent to be obtained before the interview but does not prescribe the same formalized waiver requirements.
  • Video sharing and deletion. The Illinois AIVIA includes additional protections that have no counterpart in the Maryland statute. Under the Illinois law, employers may not share applicant videos except with persons whose expertise or technology is necessary to evaluate the applicant, and employers must delete interview videos (including backup copies) within 30 days of an applicant’s request. Maryland’s Section 3-717 does not address video sharing or data deletion.

Q: What should multi-state employers take away from these laws?

An ongoing challenge for organizations operating in multiple states is the patchwork of similar laws addressing similar technologies, but sometimes with a different scope or context, along with some unique provisions.

Here, we focused on two laws that address the interview process for job applicants. One might ask whether there are other statutes that regulate the interview process in this way. Focusing only on regulation of job interviews might cause one to miss other critical compliance requirements.

The Maryland and Illinois laws discussed above may involve the collection of biometric information that, for example, also is protected under more general laws, such as the California Consumer Privacy Act (CCPA), the Illinois Biometric Information Privacy Act (BIPA), and other states with protections for such information (e.g., Colorado and Texas).

Additionally, neither the Maryland nor Illinois job interview laws includes obligations to safeguard the facial scan data collected during covered interviews. However, other state laws may include such a requirement. Maryland’s own Personal Information Protection Act (PIPA) requires:

a business that owns, maintains, or licenses personal information of an individual residing in the State [to] implement and maintain reasonable security procedures and practices that are appropriate to the nature of the personal information owned, maintained, or licensed and the nature and size of the business and its operations.

Under the PIPA, personal information includes biometric information.

It is not enough to think about just the activity the organization is engaged in – a job interview – employers need to consider a range of other issues to fully appreciate the regulatory environment for that activity – the kind of data collected, the location of the collection, who is collecting it, the state of residency of the person providing the information, how that data is collected and analyzed, among other things.

On September 2, 2026, Delaware’s Governor signed House Bill (HB) 380 and HB 381. HB 380 amends the Delaware Personal Data Privacy Act (DPDPA), which was enacted in 2023 and became effective January 1, 2025. HB 381 separately amends Delaware’s computer security breach notification law.

In short, what changes were made to the Delaware privacy and data-breach laws?

Together, the bills expand the businesses and data covered by existing law, increase protections for sensitive data, impose new vendor-management and automated decision-making requirements, and strengthen breach-notification obligations.

When do the changes take effect?

The HB 380 amendments to the DPDPA take effect January 1, 2027, while the HB 381 amendments to the breach-notification law take effect upon signing.

Which organizations does the amended DPDPA cover?

HB 380 lowers the DPDPA’s applicability thresholds. The law previously covered businesses that control or process the personal data of at least 35,000 consumers during the preceding calendar year. That threshold is now reduced to 10,000 consumers. For businesses that derive more than 20% of their gross revenue from selling personal data, the alternative threshold drops from 10,000 to 5,000 consumers.

The amendments also cause the DPDPA to apply to third parties that acquire personal data from a controller. Recall that third parties are defined broadly to include, with respect to personal data controlled by a controller, any person other than the relevant consumer, the controller of such personal data, or a processor or an affiliate of the processor or the controller.

Accordingly, organizations that fell below the original thresholds and potential third parties should reassess whether they are now subject to the DPDPA under the lower thresholds and changes enacted by HB 380. However, the changes also clarified organizations and categories of data that are excluded from the DPDPA, largely affecting financial institutions and the healthcare sector.

How did consumer rights change?

Consumer rights under the DPDPA have expanded in some significant ways. Consumers can now confirm whether controllers are including inferences about the consumer derived from personal data and processing personal data for profiling purposes to make significant decisions about the consumer.

Additionally, under the prior law, consumers had the right to obtain a list of “categories of third parties to which the controller has disclosed” their personal information. Under HB 380, consumers can obtain the list of the actual third parties, subject to several exceptions, including if the list would reveal a trade secret or that list cannot be compiled with reasonable effort. However, in that case, the controller must disclose all third parties to which it disclosed personal information.

The amendment also limits the consumer right of access with respect to certain sensitive data elements. For example, controllers may not disclose a consumer’s SSN or account password, but may only inform the consumer that the controller possesses that information.

Did the contents of the controller privacy notice change?

Yes, privacy notices must identify the controller for contact purposes, and include a description of the consumer’s personal data rights.

What new categories of sensitive data does HB 380 add?

HB 380 expands the definition of sensitive data to include national origin; health treatment or status; neural data; certain financial-account information and credentials; and government-issued identification numbers. It also covers inferences drawn from other information when those inferences are used to reveal or identify a sensitive characteristic.

What are the new requirements for processing sensitive data under Delaware law?

Processing sensitive data requires the consumer’s consent and must be reasonably necessary and proportionate to the disclosed purpose.

Are there restrictions on selling sensitive data?

Yes. A controller may sell sensitive data only when the disclosure is strictly necessary to provide or maintain a product or service affirmatively requested by the consumer. The controller must provide a clear and conspicuous notice, obtain the consumer’s consent, and retain a record of that consent for five years.

What new vendor-management obligations does HB 380 impose?

Controllers must enter into contracts with third parties receiving personal data. Those contracts must identify limited and specific purposes for the data, require the third party to provide the same level of privacy protection as the controller, and permit the controller to address unauthorized uses. Controllers must also conduct reasonable due diligence regarding third parties, including, at minimum, questionnaires and reviews of relevant documents.

What does HB 380 require for automated profiling and decision-making?

HB 380 adds requirements for profiling and reports used in decisions that produce legal or similarly significant effects, such as decisions about employment, housing, lending, insurance, education, or healthcare. When a report contributes to an adverse action, contractual provisions must require notice to the affected Delaware resident, identification of the data relied upon, and information about requesting human review where technically feasible.

Are impact assessments required for automated profiling?

Yes. Controllers engaging in covered automated profiling must conduct and document impact assessments. These assessments must address risks, inputs, outputs, performance measures, limitations, transparency, and post-deployment safeguards.

Does the employee-data exclusion still apply?

The existing employee-data exclusion is narrowed for personal data used in the context of profiling or disclosing to a third party a report for use in connection with any decision that produces legal or similarly significant effects on a resident of Delaware. In such cases, controllers and third parties have several requirements, including notice requirements to the residents concerning adverse actions, contract obligations, and additional consumer rights requests relating to personal information use in profiling.

What changes does HB 381 make to Delaware’s breach-notification law?

Like many states, the Delaware breach notification law provides an alternative way to provide notice (called “substitute notice”) when the cost of notification will exceed $75,000, the number of affected Delaware residents exceeds 100,000, or the organization does not have sufficient contact information to provide notice. Substitute notice typically involves email notice, conspicuous website notice, and notice to major statewide media. HB 381 updated the substitute notice requirement to also include notice to the Delaware Attorney General.

Additionally, in situations when an organization, through reasonable diligence, cannot identify within 60 days that personal information of Delaware residents was involved in a breach, it must provide required notification as soon as practicable after it determines such information was involved. HB 381 adds that notice to the Attorney General also must be provided within 60 days of that determination.

Does compliance with HIPAA or the Gramm-Leach-Bliley Act satisfy Delaware’s breach-notification requirements?

HB 381 narrows the existing exemption for entities regulated under laws such as HIPAA or the Gramm-Leach-Bliley Act. In short, compliance with regulator-established breach procedures now satisfies only Delaware’s 60-day timing requirement, rather than the entire state breach-notification law.

Who enforces the amended DPDPA?

The DPDPA amendments retain enforcement by the Delaware Department of Justice. The amendments do not create a private right of action.

What steps should businesses take to prepare for the new requirements?

Businesses should reassess whether they are covered under the lower applicability thresholds, inventory sensitive data and automated decision-making activities, update incident-response procedures, and review privacy notices, consent processes, third-party contracts, and vendor due diligence practices.

On June 4, 2026, Connecticut Governor Ned Lamont signed Public Act No. 26-73 (SB 472), “An Act Concerning the Electronic Surveillance of Employees,” which repeals and replaces Conn. Gen. Stat. § 31-48d. The law takes effect October 1, 2026, and significantly updates Connecticut’s longstanding requirements governing electronic monitoring of employees by employers.

Connecticut has regulated workplace electronic monitoring since 1998, and presently, several states have some form of notice, acknowledgment, and/or consent requirement for organizations engaging in electronic monitoring of their workforce.  These states include California, Delaware, Maine, New Jersey, and New York.

Before discussing the updated notice requirements, it is important to note that the new law does not change the definition of electronic monitoring. It remains:

“Electronic monitoring” means the collection of information on an employer’s premises concerning employees’ activities or communications by any means other than direct observation, including the use of a computer, telephone, wire, radio, camera, electromagnetic, photoelectronic or photo-optical systems, but not including the collection of information (A) for security purposes in common areas of the employer’s premises which are held out for use by the public, or (B) which is prohibited under state or federal law.

The use of cameras or the tracking of activities and communications on a company’s information systems quickly come to mind. However, the rapid expansion of AI technologies and the various use cases also should be assessed. Consider AI tools and use cases such as AI transcription and note taking tools, chatbots, and performance management platforms. These and other tools and use cases may require employers to revisit their notice and posting obligations under this expanded law in Connecticut.

What also remains the same is the definition of employee:

“Employee” means any person who performs services for an employer in a business of the employer, if the employer has the right to control and direct the person as to (A) the result to be accomplished by the services, and (B) the details and means by which such result is accomplished.

Updated Prior Written Notice and Posting Requirements

The updated monitoring law enhances the existing prior written notice requirements for employers engaging in electronic monitoring. Beginning October 1, 2026:

  • in addition to providing prior written notice to all employees who may be affected by electronic monitoring and specifying the types of monitoring, employers must inform those employees of the specific locations on the employer’s premises where such monitoring may occur; and
  • the existing obligation to post a notice of electronic monitoring in a conspicuous place which is readily available for viewing by employees, must also be posted in the specific location on the employer’s premises where the monitoring may occur. That posting also must describe the specific locations on the employer’s premises where the monitoring may occur.

Additionally, for employees hired on and after October 1, 2026, employers engaged in electronic monitoring must provide to such employees (prior to commencement of employment) a plain language written statement advising which activities are prohibited and may be monitored without giving prior written notice. Such activities include employees engaged in conduct which (i) violates the law, (ii) violates the legal rights of the employer or the employer’s employees, or (iii) creates a hostile workplace environment, and for which electronic monitoring can produce evidence of this misconduct.

Notably, the requirement to disclose the specific location of the premises being monitored does not apply where the premises is an airport, or when the employer has reasonable grounds to conduct such monitoring for security and employee safety purposes.

The updated monitoring law did not change the enforcement provisions. The Labor Commissioner may impose a civil penalty on any person that violates the notice and posting requirements. The maximum penalties are $500 for the first offense, $1,000 for the second, and $3,000 for the third and subsequent offenses.

Connecticut employers should review their monitoring activities, including deployments of AI tools and their respective use cases, and assess compliance with applicable posting, notice, and/or acknowledgment requirements in Connecticut and other states as applicable.

A family’s ordinary afternoon was shattered when an unknown number added multiple relatives, including a teenager, to a group chat and shared what appeared to be AI-generated explicit images of a family member, the Wall Street Journal (WSJ) reported. The goal was simple: to extort money by threatening to release the images more widely. The scheme was sophisticated, leveraging publicly available social media photos and AI tools to fabricate convincing pornographic content and to map out family relationships for maximum emotional impact.

Why This Matters for Your Organization

Sextortion, generally speaking, is the use of real or fabricated explicit images to coerce victims into paying money. According to reports, the practice is accelerating, and AI is the catalyst. Scammers no longer need to manually research their targets. Open-weight AI models running on dedicated machines can scrape social media profiles, analyze public data, and piece together personal relationships at scale.

What does this mean for organizations?  Whether the target is the employee or the organization, the organization could face significant disruption to the business, distracted employees, and reputational harm. Reported tactics by online extortionists include threats to post or send explicit imagery of employees in places online designed to be seen by the organization and its customers, such as social media platforms or, as in the scenario reported in the WSJ, by group text. Much the same as threat actors who plan spear phishing attacks, sextortionists do their research in order to understand and leverage their victims’ connections. The result could be a demand to the organization for large sums paid in cryptocurrency, in exchange for keeping the images fake though they may be, out of the public eye.

In addition to facing an extortion demand and the risk of harm to the brand and reputation, organizations also need to consider the impact on the victim employee(s). These kinds of attacks can cause the subject employees severe emotional distress distracting them from their job. The employee’s personal and business accounts, including email, also may have been compromised, helping the threat actor to expand the impact of the attack.

Are You Prepared?

Many organizations have robust cybersecurity protocols for protecting corporate systems, but far fewer address the human side of digital exploitation. Here are the questions every organization should be asking today:

  • Do your employees know what sextortion looks like? Many people still assume they aren’t targets because they aren’t wealthy or famous. The reality is that these AI-driven scams are automated and opportunistic— no one is too small a target. Consider updating your training programs to address this threat.
  • Does your security awareness training cover AI-generated threats? Traditional phishing training may not address the emotional manipulation involved in sextortion or the use of deep-fake technology to create convincing explicit images.
  • Do your employees know what to do if it happens to them? Experts, including the FBI, advise victims not to pay, to block and report the scammer to the FBI’s Internet Crime Complaint Center, and to immediately change passwords and end unknown device sessions. Does your organization have clear guidance or an employee assistance program that covers this type of incident?
  • Are you encouraging good digital hygiene? Simple steps—setting social media accounts to private, using strong and unique passwords, and enabling two-factor authentication—can significantly reduce exposure.
  • Does your incident response plan address this threat? Preparedness is critical for any significant business threat. In addition to ensuring there is a clear path for employees to report these incidents confidentially, whether they occur through personal or corporate channels, businesses should expand their incident response plan. They also should practice how they might respond to such an attack, which would know knowing what resources they have to provide support for the organization and affected employees. 

The Bottom Line

AI is supercharging old scams into something faster, more convincing, and more invasive. Sextortion is no longer a risk that only affects teenagers or public figures. It can reach anyone through any group chat, at any time. Organizations should consider this risk and improve preparedness.

A broad coalition of artificial intelligence developers, cybersecurity companies, financial institutions, technology providers, and other organizations has issued an open letter calling for a coordinated effort to strengthen cyber defenses.

“We have a limited window to strengthen cyber defenses.”

The letter warns that AI-enabled cyberattacks have become more widespread and sophisticated. At the same time, it argues that advances in AI can help defenders identify vulnerabilities, remediate weaknesses, and respond to incidents more efficiently. Importantly, the letter points to several industries facing significantly higher levels of risk for organizations in those industries and the sometimes many thousands or millions of people they serve, e.g., critical infrastructure, manufacturing, supply chain, utilities (water), health care.

The signatories propose three overarching principles:

  1. Recognize that existing security practices may no longer be sufficient;
  2. Expand access to AI-enabled defensive capabilities; and
  3. Build a collective response involving businesses, technology providers, governments, and frontier AI companies.

While not a new recommendation, the letter calls for cybersecurity to become an “immediate leadership priority.” It advocates that particular attention be given to high-risk vulnerabilities, least-privilege access, strong authentication, layered defenses, and security standards for technology that organizations purchase, develop, or deploy. In short, the letter suggests that the measures for achieving the standard of “reasonable safeguards” may have changed as the threat landscape rapidly evolves, and so too must the measures for safeguarding assets from those threats.  What constitutes “reasonable safeguards” is now a fast-moving target.

For those responsible for cybersecurity preparedness and incident response, the letter reinforces an important point: Organizations should not view AI defense as simply a technology-acquisition project. It is a governance, legal-risk, and operational-resilience issue. New tools will not compensate for unclear responsibility, incomplete asset inventories, weak vendor oversight, or incident-response plans that have never been tested. Organizations also should evaluate AI security tools carefully, including what data the tools collect, where that data is stored and how it is safeguarded, how model outputs are validated, and whether contracts appropriately allocate responsibility for security incidents.  

Taking these steps, among others, will help organizations make the best use of this limited window to strengthen their cyber defenses, positioning them as less vulnerable targets for AI-powered cyberattacks and to defend themselves against the class action lawsuits that are likely to become even more prevalent as these attacks gain steam.