California has enacted Senate Bill (SB) 690, which narrows the circumstances under which private parties may bring lawsuits under the California Invasion of Privacy Act (CIPA), Cal. Penal Code Section 638.51.

The new law takes effect January 1, 2027, and notably includes a two-year look-back period for pending lawsuits commenced before the law was enacted.

Brief History

CIPA, enacted in 1967, includes civil and criminal provisions and, importantly, allows private parties to enforce the law.  The law also allows those private parties to recover at least $5,000 per violation.  CIPA generally prohibits the interception and use of the contents of a communication without the consent of all parties to the communication.  Subject to narrow exceptions, the law also prohibits the installation or use of a “pen register” or “trap and trace device” without a court order or consent of all parties whose communication might be captured by those devices.
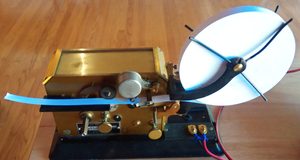
Pen register. Manufactured by J. H. Bunnell & Co., Brooklyn, New York. Mid-20th century. Image licensed under the Creative Commons Attribution-Share Alike 4.0 International license.

Plaintiffs Have Targeted Websites

Although terms in the law like “pen register” or “trap and trace device”  referred to physical devices used to collect telephone dialing and routing information on a landline telephone network, plaintiffs have increasingly alleged that this provision should apply to common website technologies, such as cookies, pixels, and tags, under the theory that those technologies capture information about the website visitor and their activity similar to a pen register and trap and trace device.

CIPA allows an injured person to recover statutory damages of $5,000 per violation or three times the amount of actual damages, whichever is greater. A plaintiff generally does not need to prove actual damages. As a result, businesses of various sizes have faced lawsuits, arbitration demands, and prelitigation notices alleging that their websites and the technologies deployed on their websites violated CIPA by collecting visitors’ digital routing, addressing, or signaling information.

Relief for Businesses

SB 690 eliminates the private right of action under the “pen register” or “trap and trace device”  provisions of the law against digital properties. Under the amendment, only the California Attorney General may bring an action under CIPA’s civil-remedies provision against a private actor for an alleged violation arising from conduct occurring on an internet website, online application, or mobile application. The limitation also applies retroactively to pending claims in actions commenced during the two years preceding the law’s operative date.

SB 690 did not repeal CIPA’s restrictions on pen registers and trap and trace devices. Instead, it changes who may pursue civil remedies for this defined category of online conduct.

SB 690 also does not eliminate private lawsuits involving other provisions of CIPA, including certain claims alleging unauthorized wiretapping or the recording or use of confidential communications.

Businesses should therefore avoid treating SB 690 as a general exemption for website tracking technologies. Companies should continue reviewing the cookies, pixels, analytics tools, chat functions, session-replay software, and other third-party technologies deployed on their websites and applications.

Print:
Email this postTweet this postLike this postShare this post on LinkedIn
Photo of Jason C. Gavejian Jason C. Gavejian

Jason C. Gavejian is the office managing principal of the Berkeley Heights, New Jersey, office of Jackson Lewis P.C. and a member of the firm’s Board of Directors. He is also a Certified Information Privacy Professional (CIPP/US) with the International Association of Privacy…

Jason C. Gavejian is the office managing principal of the Berkeley Heights, New Jersey, office of Jackson Lewis P.C. and a member of the firm’s Board of Directors. He is also a Certified Information Privacy Professional (CIPP/US) with the International Association of Privacy Professionals.

As a Certified Information Privacy Professional (CIPP/US), Jason focuses on the matrix of laws governing privacy, security, and management of data. Jason is co-editor of, and a regular contributor to, the firm’s Privacy blog.

Jason’s work in the area of privacy and data security includes counseling international, national, and regional companies on the vast array of privacy and security mandates, preventive measures, policies, procedures, and best practices. This includes, but is not limited to, the privacy and security requirements under state, federal, and international law (e.g., HIPAA/HITECH, GDPR, California Consumer Privacy Act (CCPA), FTC Act, ECPA, SCA, GLBA etc.). Jason helps companies in all industries to assess information risk and security as part of the development and implementation of comprehensive data security safeguards including written information security programs (WISP). Additionally, Jason assists companies in analyzing issues related to: electronic communications, social media, electronic signatures (ESIGN/UETA), monitoring and recording (GPS, video, audio, etc.), biometrics, and bring your own device (BYOD) and company owned personally enabled device (COPE) programs, including policies and procedures to address same. He regularly advises clients on compliance issues under the Telephone Consumer Protection Act (TCPA) and has represented clients in suits, including class actions, brought in various jurisdictions throughout the country under the TCPA.

Photo of Joseph J. Lazzarotti Joseph J. Lazzarotti

Joseph J. Lazzarotti is a principal in the Tampa, Florida, office of Jackson Lewis P.C. He founded and currently co-leads the firm’s Privacy, Data and Cybersecurity practice group, edits the firm’s Privacy Blog, and is a Certified Information Privacy Professional (CIPP) with the…

Joseph J. Lazzarotti is a principal in the Tampa, Florida, office of Jackson Lewis P.C. He founded and currently co-leads the firm’s Privacy, Data and Cybersecurity practice group, edits the firm’s Privacy Blog, and is a Certified Information Privacy Professional (CIPP) with the International Association of Privacy Professionals. Trained as an employee benefits lawyer, focused on compliance, Joe also is a member of the firm’s Employee Benefits practice group.

In short, his practice focuses on the matrix of laws governing the privacy, security, and management of data, as well as the impact and regulation of social media. He also counsels companies on compliance, fiduciary, taxation, and administrative matters with respect to employee benefit plans.

Photo of Shannon Bettis Nakabayashi Shannon Bettis Nakabayashi

Shannon Bettis Nakabayashi is a principal in the San Francisco, California, office of Jackson Lewis P.C. She is a core member of the firm’s California Class and PAGA Actions Resource Group.  She specializes in wage and hour complex litigation.

Shannon has extensive experience…

Shannon Bettis Nakabayashi is a principal in the San Francisco, California, office of Jackson Lewis P.C. She is a core member of the firm’s California Class and PAGA Actions Resource Group.  She specializes in wage and hour complex litigation.

Shannon has extensive experience litigating class, collective and PAGA matters in state and federal courts and in arbitrations. Shannon frequently represents employers in the hospitality, retail and healthcare fields and she specializes in the unique wage and hour regulations that apply to the healthcare and staffing industries.  Her litigation experience includes handling class and PAGA actions for overtime misclassification, independent contractor misclassification, unpaid wages, overtime, regular rate of pay, rounding, tips and services charges, wage statements, bonus calculations, commissions, paid sick leave, alternative workweek schedules, timekeeping and penalties.

Shannon is a member of the firm’s Privacy, Data & Cybersecurity practice group and regularly handles FCRA and TCPA class actions.

Photo of Damon W. Silver Damon W. Silver

Damon W. Silver is a principal in the New York City, New York, office of Jackson Lewis P.C. and co-leader of the firm’s Privacy, AI & Cybersecurity practice group. He is a Certified Information Privacy Professional (CIPP/US).

Damon helps clients across various industries—with…

Damon W. Silver is a principal in the New York City, New York, office of Jackson Lewis P.C. and co-leader of the firm’s Privacy, AI & Cybersecurity practice group. He is a Certified Information Privacy Professional (CIPP/US).

Damon helps clients across various industries—with a focus on financial services, healthcare, and education—handle their data safely. He works with them to pragmatically navigate the challenges they face from cyberattacks, technological developments including AI, a fast-evolving data privacy and security legal compliance landscape, and an active and innovative plaintiffs’ bar.

Damon recognizes that needs vary from one client to the next. Large, mature organizations, for instance, may need assistance managing multi-jurisdictional and multi-faceted compliance obligations. Others may be in a stage of development where their greatest need is to triage what must be done now and what can more safely be left for later. Damon takes the time to understand each client’s circumstances and priorities and then works with it to develop tailored approaches to effectively managing risk without unnecessarily hindering business operations.

Photo of Ken K. Suh Ken K. Suh

Kenneth (Ken) Suh is a principal in the Chicago office of Jackson Lewis P.C. He has a long track record of successfully representing clients through complex legal issues inherent to unsettled areas of law and emerging technologies, including cybersecurity, data privacy, artificial intelligence…

Kenneth (Ken) Suh is a principal in the Chicago office of Jackson Lewis P.C. He has a long track record of successfully representing clients through complex legal issues inherent to unsettled areas of law and emerging technologies, including cybersecurity, data privacy, artificial intelligence, and intellectual property. Whether in the courtroom as lead counsel on a tech E&O case or guiding clients in establishing AI governance frameworks, his unique blend of business, engineering, and legal experience allows him to effectively communicate and bring together stakeholders from multiple disciplines.

An experienced litigator with trial experience, Ken works closely with clients to drive successful, business focused results for his clients. While many cases resolve prior to trial, Ken understands that trial-focused litigation strategies drive the best results for clients. His litigation experience includes privacy and data breach class actions (BIPA, CIPA/wiretapping, pixel, and FCRA/FACTA), tech E&O disputes (software and hardware implementation, tech design, and Artificial Intelligence), and intellectual property cases (copyrights, trademarks, and patents).

Photo of Daniel R. Overstreet Daniel R. Overstreet

Daniel Overstreet is an Associate in the Orange County, California office. He counsels and defends employers in all aspects of California employment law, including single-plaintiff actions centered on harassment, retaliation, discrimination, wrongful termination, disability accommodations, and wage-and-hour violations, in addition to class actions.…

Daniel Overstreet is an Associate in the Orange County, California office. He counsels and defends employers in all aspects of California employment law, including single-plaintiff actions centered on harassment, retaliation, discrimination, wrongful termination, disability accommodations, and wage-and-hour violations, in addition to class actions.

Daniel advises clients with the understanding that not all cases are the same, nor will all clients share the same objectives. He approaches each case with a fresh perspective, working closely with clients to establish their key objectives and develop a strategy for handling each case that advances those objectives. Whether navigating complex workplace investigations, advising on compliance with California’s intricate labor laws, or representing clients in litigation, Daniel provides strategic and effective solutions. Clients can rely on Daniel’s commitment to clear communication, thorough preparation, and relentless advocacy. Daniel has experience in all aspects of litigation handling, including client interviews, factual investigation, discovery, depositions, and motion practice.

Privacy and Cybersecurity Experience – Daniel also has experience defending data privacy claims, including claims brought under the California Invasion of Privacy Act, the Telephone Consumer Protection Act, the Federal Wiretap Act, the California Computer Data Access and Fraud Act, and common law invasion of privacy claims, both on an individual and class basis.